HIPAA and Privacy in a Gym-Based PT Practice
A closed door is privacy in the physical sense, and it is not the same thing as HIPAA compliance. Training or treating patients inside a private room, rather than on an open gym floor, protects what people say and how they move from an audience, but the federal privacy obligations a healthcare provider owes patients travel with the provider’s own practice, not with the room. Understanding which is which matters before you see your first patient in a rented space instead of a clinic or a mobile visit.
What the rule says
HIPAA’s privacy protections attach to covered entities and their business associates, generally providers, health plans and clearinghouses that transmit health information electronically in connection with certain standard transactions, checked September 2026. Whether a specific cash-based practice counts as a covered entity turns on how it bills and what it transmits, a determination that belongs with a healthcare attorney or compliance consultant, not a website. Indiana adds no separate state privacy statute in the fact base behind this page for a movement-only practice operating outside a clinic; where one might apply is itself a question for that attorney. This is general information, not legal advice, and the answer can change with how your practice actually operates.
What a private room genuinely protects
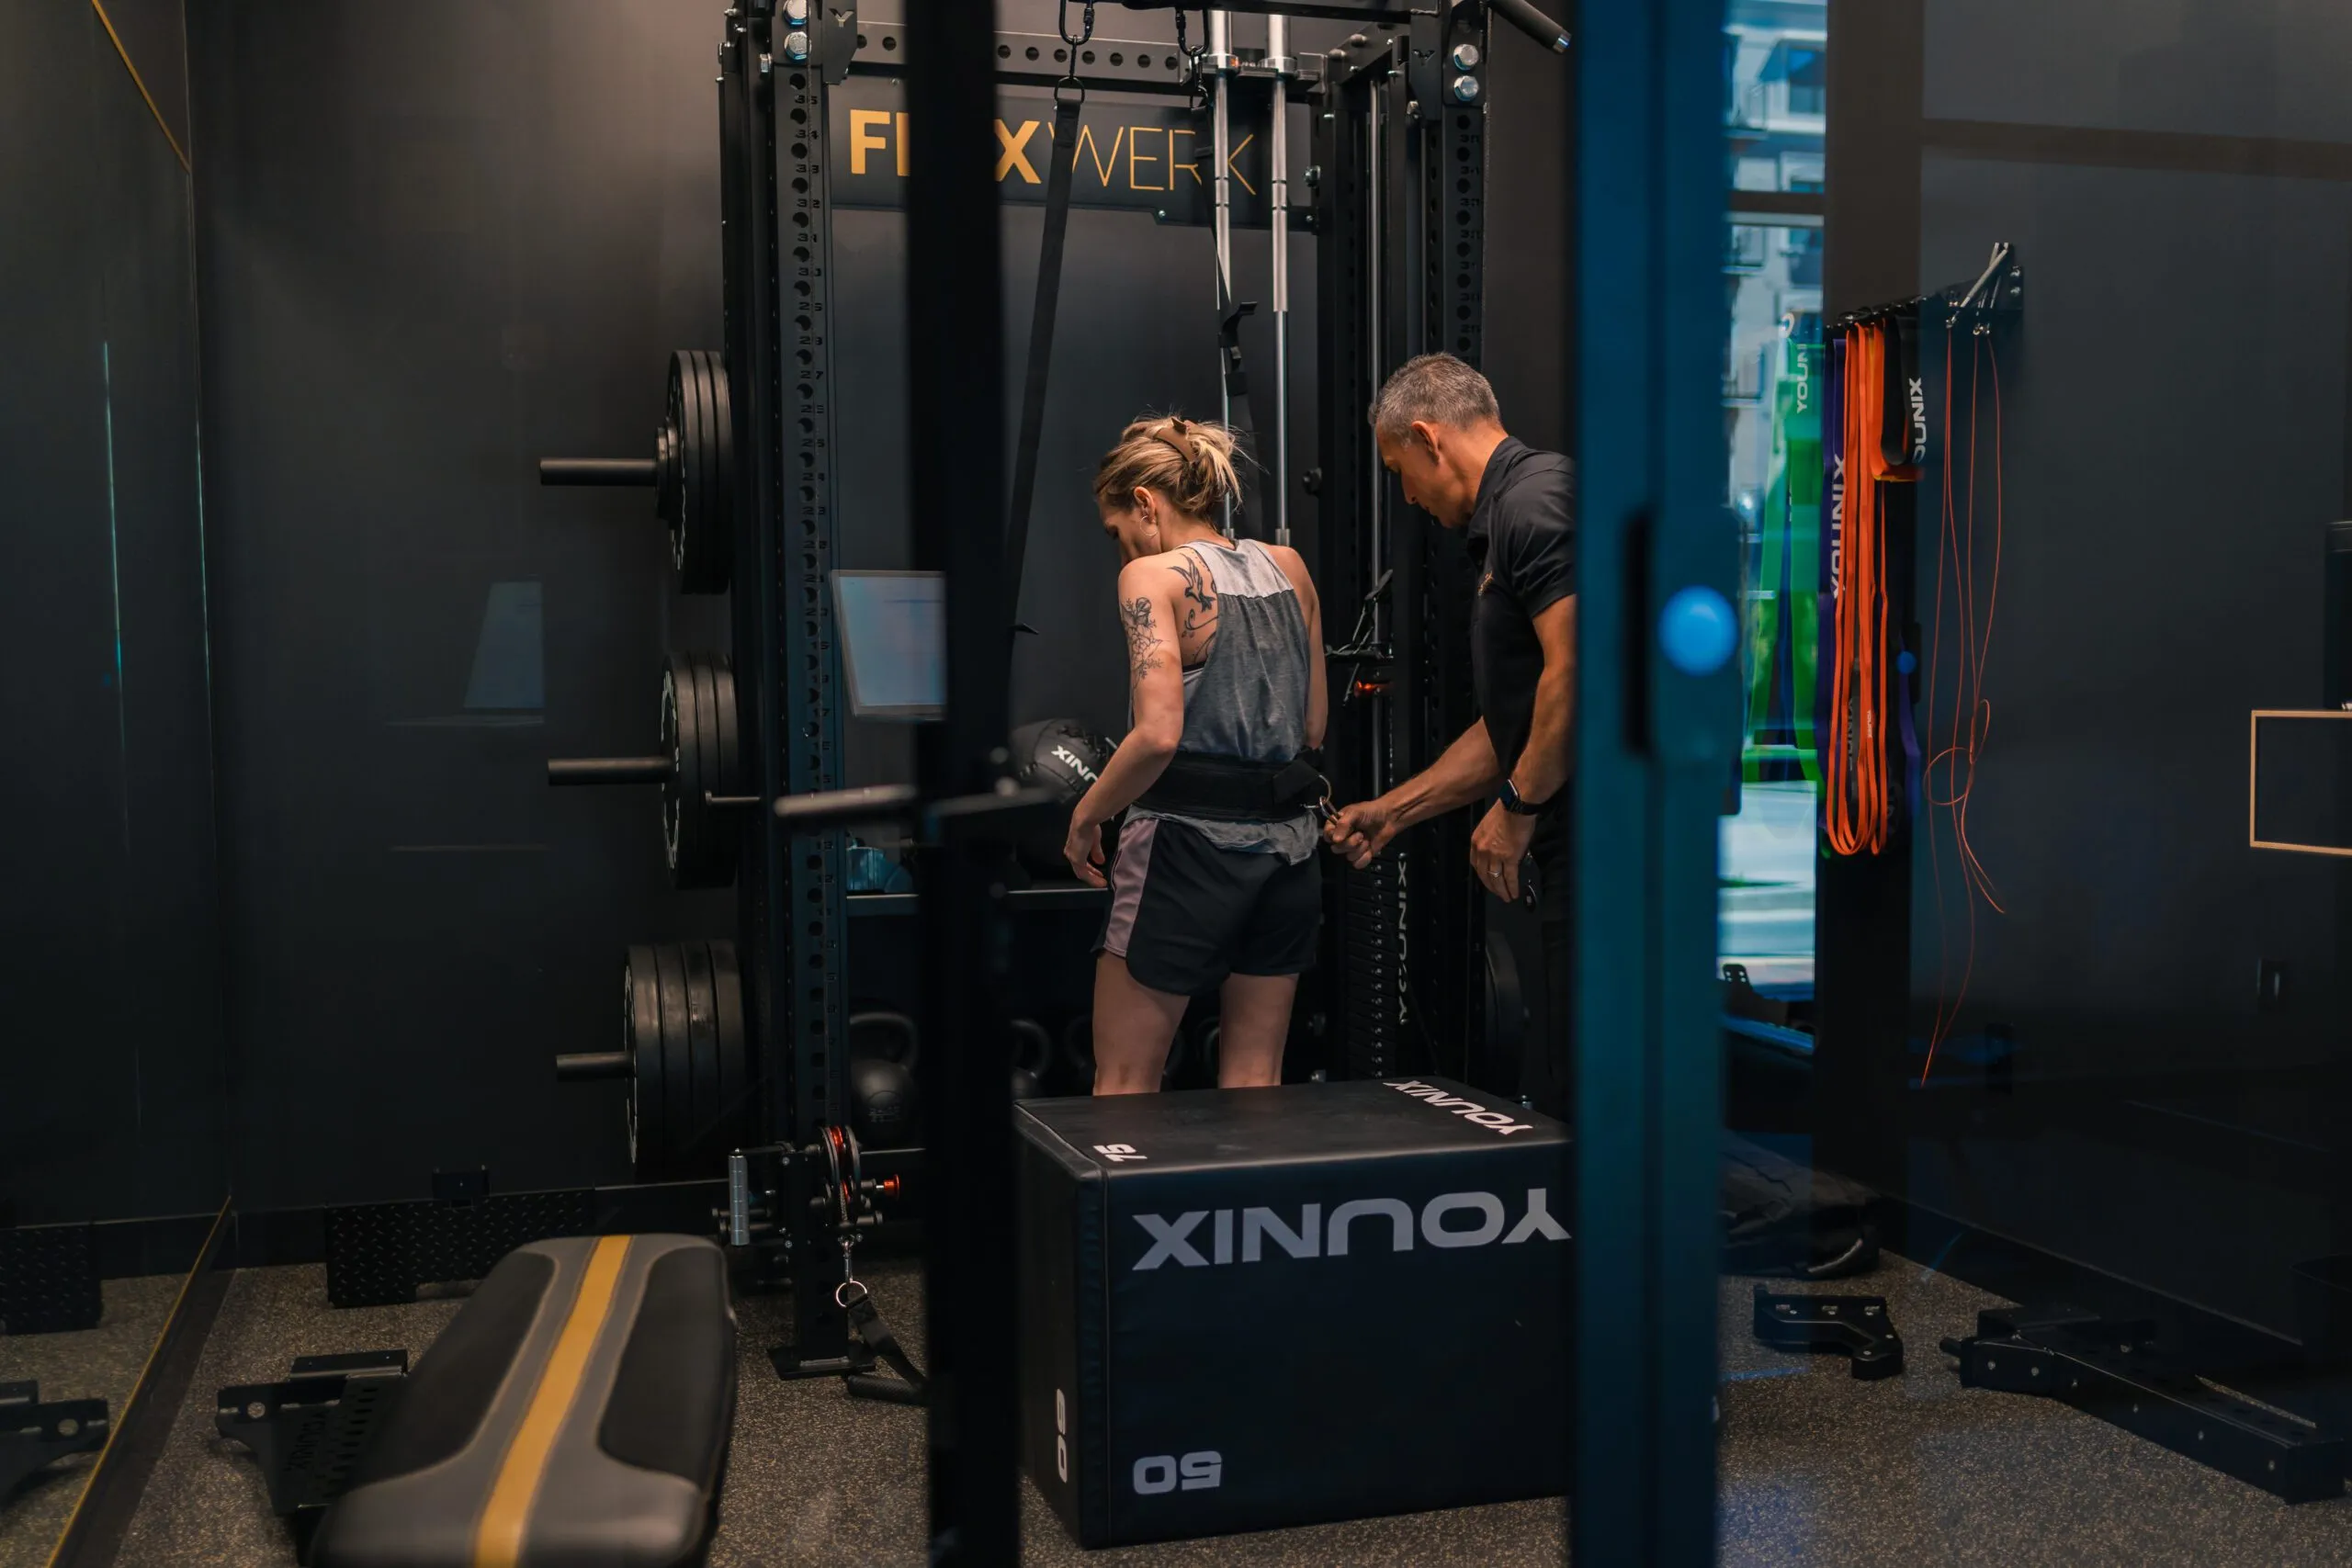
The room does real work on the physical side of privacy. A door that closes keeps a pain history, a diagnosis conversation, or an unsteady first attempt at a movement away from strangers on an open floor, the same protection a private treatment room offers any licensed provider working outside a clinic. What it does not do is store records securely, encrypt anything, or manage who on your team can see a chart. Those safeguards live in your own systems, not in the four walls of a rented room.
What stays entirely on the provider
Four things do not move with the room, ever: your documentation platform and whether it meets the standards your compliance obligations require, your consent forms, who on your team can access a given patient’s file, and how you dispose of anything printed. FlexWerk supplies private space and no clinical oversight of any kind, so a provider’s compliance program has to be complete before the first patient walks through the door, exactly as it would in a clinic.
Building the habit in a shared building
A shared facility adds one practical wrinkle worth planning for: other professionals are in nearby rooms, and hallways are not exam rooms. Keep any conversation involving a patient’s health history inside the closed door, carry paper files rather than leaving them visible, and confirm your specific setup with your compliance advisor before relying on the room alone. The scope and documentation question that sits next to this one, wellness versus treatment, uses the same discipline: decide the standard first, then document to it.
Treat the room as one layer of privacy among several, confirm the compliance layer with a professional who knows your specific billing and systems, and walk in on day one with both already built.
Related questions
Is FlexWerk responsible for HIPAA compliance in the room?
No. FlexWerk provides private space and no clinical oversight, so documentation, consent, data security and every other compliance obligation stay with the treating provider.
Does training in a private room make my practice HIPAA compliant automatically?
No. Privacy in the room is physical, not administrative. Compliance depends on your own systems, forms and data handling, which a private room does not create by itself.
Who should I ask whether HIPAA applies to my specific practice?
A healthcare attorney or compliance consultant familiar with how your practice bills and transmits information. This page is general information, not legal advice, and the answer is specific to your setup.